Discover & Normalize
ค้นหา Asset และรวม Event จาก Cloud, Network, Server, Endpoint, Application และ OT
รวม Event, Performance และ Configuration จาก IT และ OT Infrastructure เพื่อทำ Correlation, UEBA, Incident response และ Compliance จากมุมมองเดียว
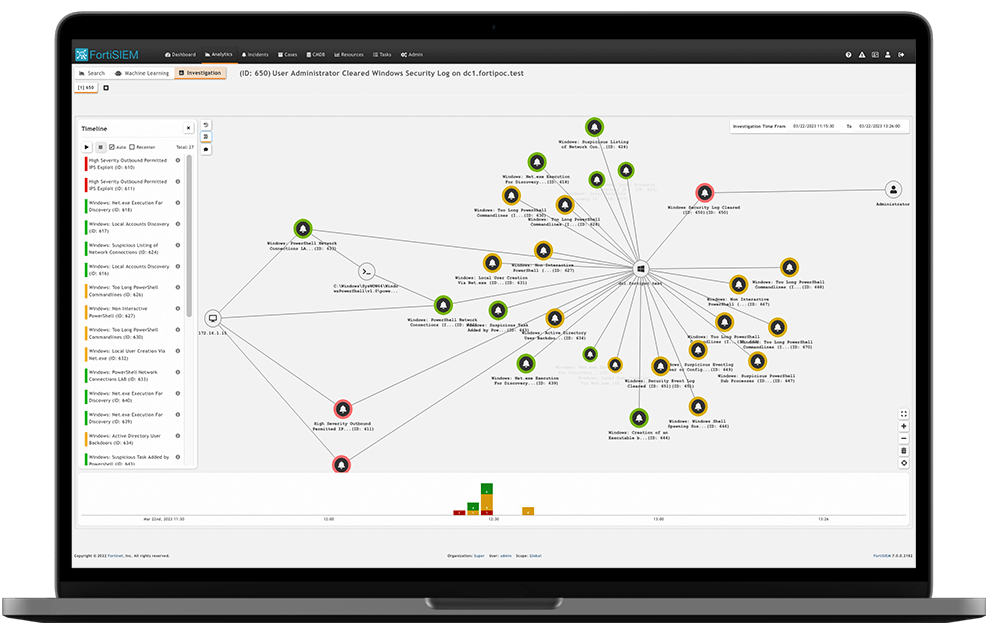
FortiSIEM รวม Discovery, CMDB, Event collection, Analytics, UEBA และ SOAR เพื่อให้ SOC เห็น Dependency ของ IT/OT Infrastructure และตอบสนองจาก Context เดียวกัน
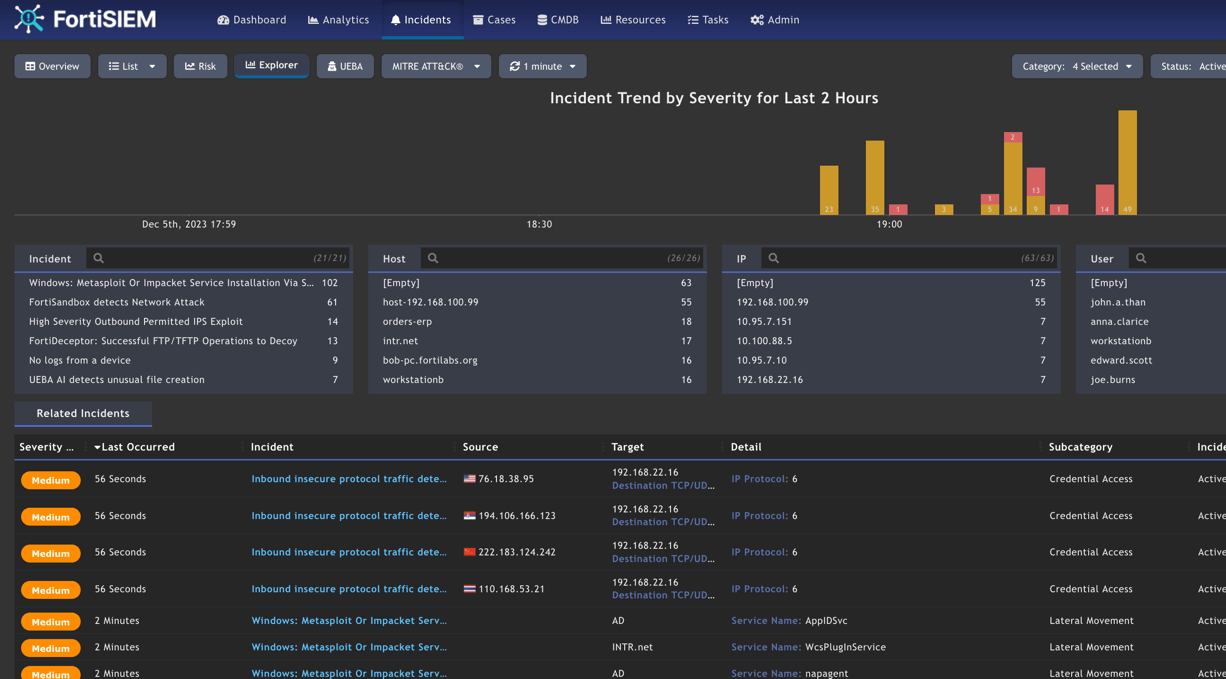
ค้นหา Asset และรวม Event จาก Cloud, Network, Server, Endpoint, Application และ OT
เชื่อม Event กับ CMDB, Topology และ Threat context เพื่อแยก Incident สำคัญจาก Noise
ใช้ Rules และ UEBA ตรวจจับพฤติกรรมผิดปกติของผู้ใช้ อุปกรณ์ และ Workload
จัดการ Case และใช้ Automation หรือ Playbook เพื่อประสาน Response กับ Security Fabric
สามารถออกแบบได้ทั้ง Hardware, Virtual, SaaS และ Hybrid ตาม Data volume กับข้อกำหนดขององค์กร
รวบรวม Event และ Performance Data ใกล้แหล่งข้อมูลก่อนส่งเข้าสู่ Supervisor
500 SNMP / 200 WMI performanceSupervisor สำหรับองค์กรที่ต้องการ Correlation, Analytics และ UEBA แบบรวมศูนย์
Distributed collectionเพิ่ม Event throughput สำหรับ SOC และ Hybrid Infrastructure ขนาดใหญ่
Distributed collectionส่งข้อมูลจำนวนผู้ใช้ อุปกรณ์ Traffic, Retention, Site และระบบเดิม ทีม CloudThing จะช่วยวาง Architecture, Sizing และ Scope สำหรับ Pilot