Discover
มองเห็นอุปกรณ์ Wired และ Wireless พร้อมจำแนกประเภท เจ้าของ และพฤติกรรม
สร้าง Visibility ของอุปกรณ์ทุกชนิด ควบคุมสิทธิ์ตาม Identity และ Risk พร้อมตอบสนองอัตโนมัติเมื่ออุปกรณ์ไม่เป็นไปตาม Policy
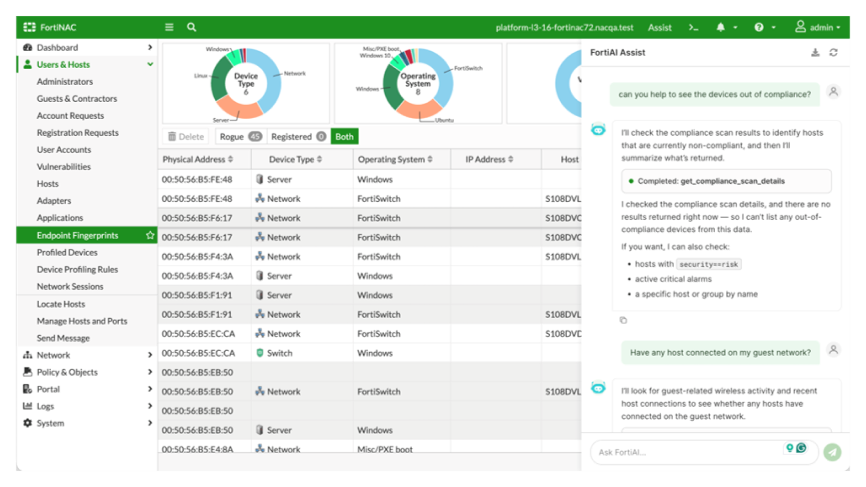
FortiNAC ค้นหาและจำแนก IT, IoT, OT และ IoMT Devices จากนั้นใช้ Identity, Posture และ Risk เพื่อกำหนด Network access และสั่ง Quarantine หรือ Remediation อัตโนมัติ
มองเห็นอุปกรณ์ Wired และ Wireless พร้อมจำแนกประเภท เจ้าของ และพฤติกรรม
ตรวจ Identity, Security posture, Vulnerability และ Compliance ก่อนอนุญาตเชื่อมต่อ
กำหนด Role, Network segment และ Policy ตามผู้ใช้ อุปกรณ์ สถานที่ และระดับความเสี่ยง
เปลี่ยนสิทธิ์ กักกัน หรือเปิด Workflow แก้ไขเมื่อพบพฤติกรรมที่ผิดปกติ
Sizing ใช้จำนวน Switch ports รวมกับจำนวน Wireless clients สูงสุดที่เชื่อมต่อพร้อมกัน
รวม Control และ Application Server สำหรับองค์กรหรือไซต์ขนาดเล็ก
เพิ่ม Capacity สำหรับ Campus ขนาดกลางที่มีอุปกรณ์ Wired และ Wireless จำนวนมาก
เหมาะกับระบบขนาดใหญ่และสภาพแวดล้อมที่มี Persistent Agent จำนวนไม่มาก
บริหาร FortiNAC Control & Application Servers หลายไซต์จากศูนย์กลาง
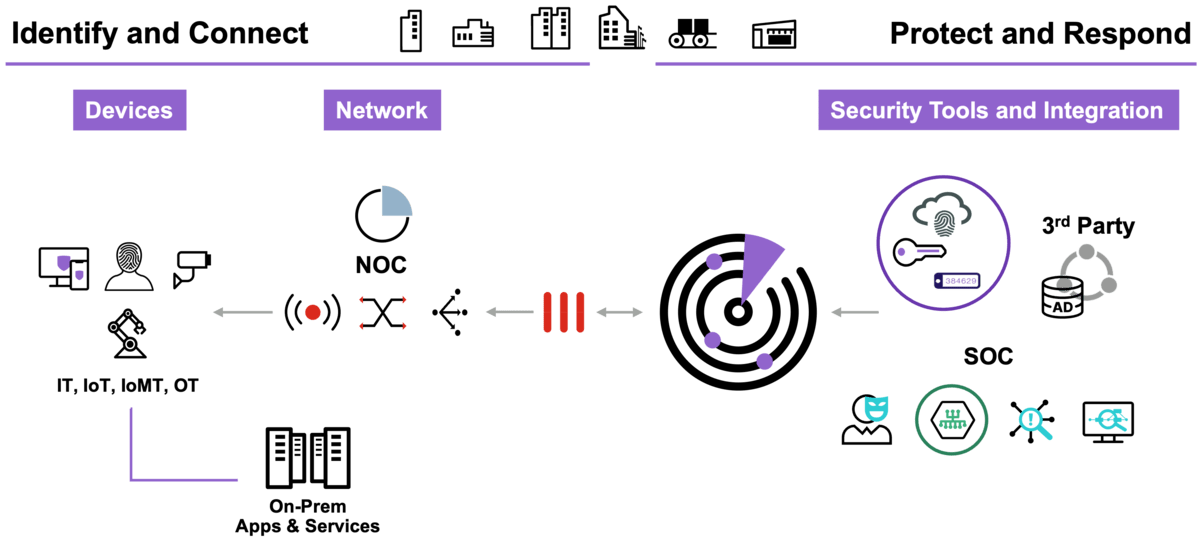
ส่งข้อมูลจำนวนผู้ใช้ อุปกรณ์ Traffic, Retention, Site และระบบเดิม ทีม CloudThing จะช่วยวาง Architecture, Sizing และ Scope สำหรับ Pilot