Identity sources
เชื่อม Directory, IdP, MDM และ Certificate เพื่อระบุตัวตนผู้ใช้กับอุปกรณ์
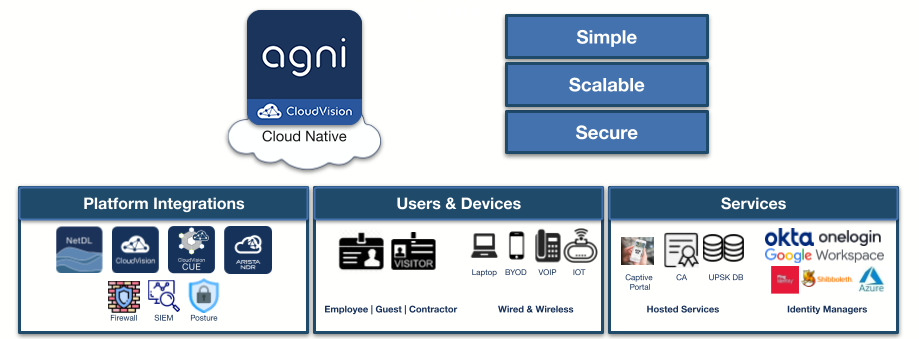
Arista Guardian for Network Identity (AGNI) เป็น NAC ที่เชื่อม User, Endpoint และ IoT เข้ากับ Policy กลาง พร้อม Profiling, Continuous posture และ Microsegmentation สำหรับ Wired และ Wireless แบบ Multi-vendor
Architecture ถูกแบ่งเป็น Layer ที่ชัดเจน เพื่อเลือกเริ่มจากส่วนที่จำเป็นและเชื่อมต่อกับระบบเดิมขององค์กรได้
เชื่อม Directory, IdP, MDM และ Certificate เพื่อระบุตัวตนผู้ใช้กับอุปกรณ์
ประเมิน Identity, Device profile, Posture, Location และ Risk ก่อนกำหนดสิทธิ์
ทำ AAA ผ่าน RadSec หรือ RADIUS และส่ง Role/Segment ไปยัง Wired กับ Wireless infrastructure
ติดตาม Context หลังเชื่อมต่อและเปลี่ยน Policy เมื่อ Posture หรือ Risk เปลี่ยน
เลือกใช้ตาม Outcome, Operating model และข้อจำกัดของระบบจริง โดยไม่จำเป็นต้องเปิดใช้ทุกส่วนพร้อมกัน
จำแนก Managed, Unmanaged, IoT และ Guest device เพื่อกำหนด Onboarding flow ที่เหมาะสม
ประเมิน Health และ Compliance ก่อนและระหว่างการเชื่อมต่อ Network
ใช้ MSS และ UPSK แยกสิทธิ์ตาม User, Device และ Application โดยไม่ต้องพึ่ง VLAN จำนวนมาก
รองรับ Multi-vendor network พร้อม API และ Pub/Sub สำหรับเชื่อม Security ecosystem
รายการนี้ใช้เป็นแกนสำหรับ Architecture workshop การเลือก SKU, License และ Sizing จริงต้องตรวจสอบ Requirement กับ Datasheet รุ่นล่าสุดอีกครั้ง
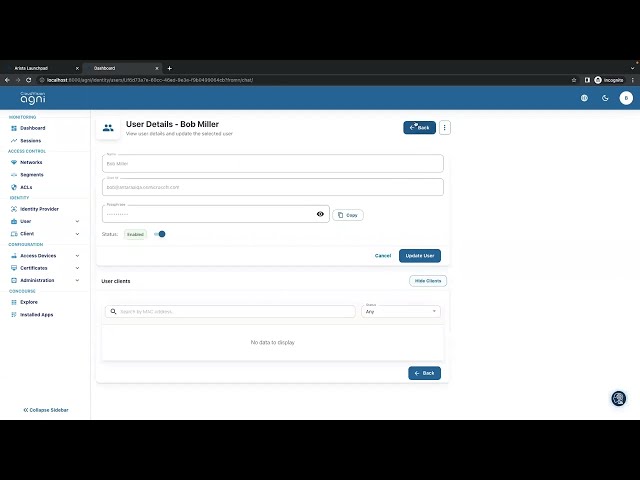
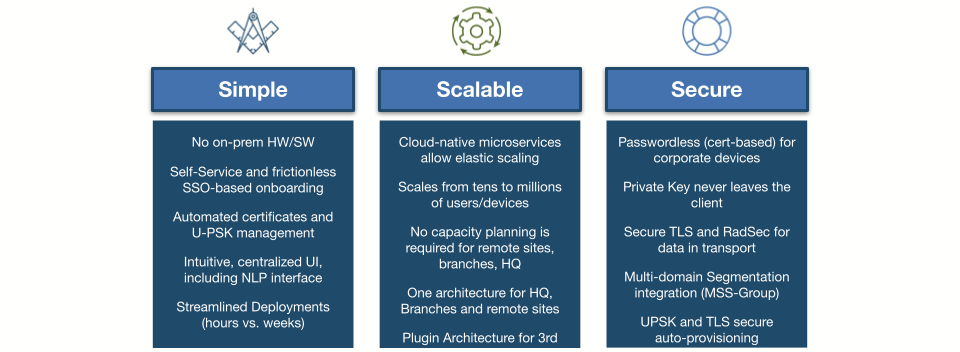
NAC แบบ Cloud-native ลดภาระติดตั้ง Infrastructure และรองรับหลาย Site จาก Policy กลาง
วาง Management และ Policy service ภายในสำหรับข้อกำหนด Data residency หรือ Network isolation
ประกอบ Policy จาก Identity, Profile, Posture, Location, Time และ Risk
เตรียมจำนวน Site, User, Device, Application, Link, Identity source และระบบเดิม เพื่อวาง Architecture, License และ Pilot scope ร่วมกัน